§ 01Identity
Identity and access.
Single sign-on, role-based access control with workspace roles and groups, and admin-gated settings.

Single sign-on, role-based access, scoped service tokens, key rotation, PII masking, cost ceilings, and a daily digest, the controls that move a pilot from “interesting” to “approved.”

Single sign-on, role-based access control with workspace roles and groups, and admin-gated settings.
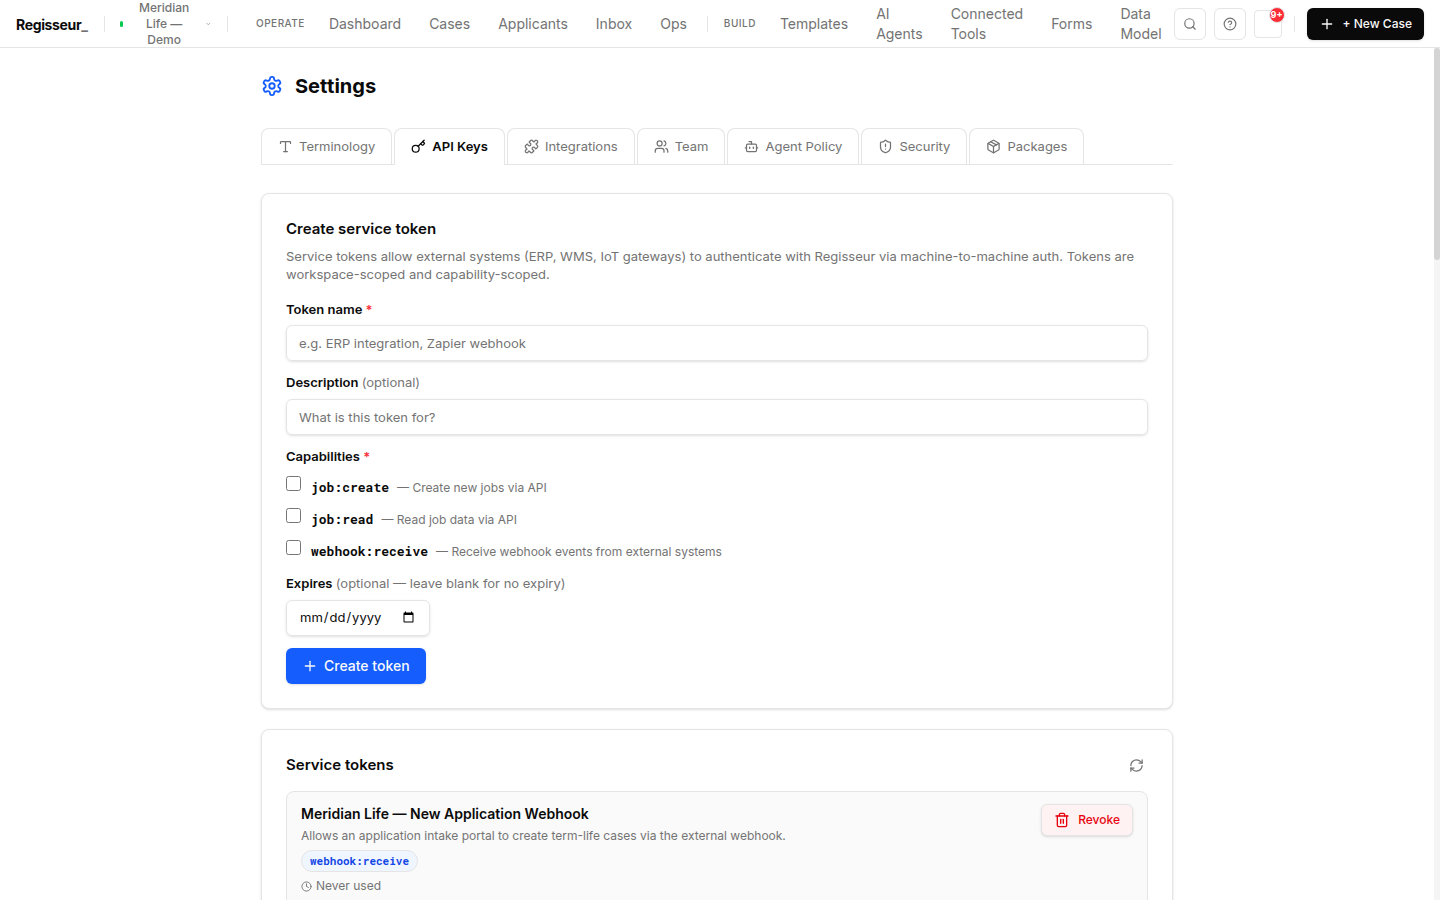
Scoped service tokens let other systems call Regisseur without ever issuing them a user identity. External callers never get user credentials. Credentials are stored in a managed secret backend with key rotation built in.
PII/PHI masking is configurable per workspace and applied before prompt assembly: redaction as a compiler pass, not a runtime hope. Data stays inside your deployment, in your region; per-workspace retention.

Set budget ceilings per workspace; the per-job circuit breaker enforces runaway-cost limits. Cost is measured on real token usage, never fabricated.

A daily digest summarizes what happened and what needs attention; ops trends show throughput, cycle time, and SLA health over time.

Bring your security and compliance checklist. We'll walk identity, scoped tokens, masking, cost ceilings, and the audit surface, and send the security & compliance package for your review.